Rethinking Security: How Autonomous AI Challenges Traditional Models
We have moved beyond when conversational AI was just a fancy chatbot. Now, the real frontier of artificial intelligence is autonomous execution, not just answering questions or drafting emails.
Today’s AI agents can call APIs, access sensitive databases, set up cloud infrastructure, change system settings, create new digital identities, and run code in real time. They do more than just talk—they take action.
This change turns AI from a passive source of answers into an active digital worker. It also brings a serious challenge. Traditional security systems were designed for people, not fast, autonomous systems. How do you protect something that operates at machine speed, has wide digital access, and makes its own decisions?
This is where Identity, Security, and AI converge.
The Paradigm Shift: From Human Intent to Machine Autonomy
In older enterprise security models, every important action like updating a database, moving money, or changing permissions required human involvement. Even when using service accounts or API keys, a person still set up the process.
Autonomous agents change this approach. When an agent can create its own sub-identities and buy cloud resources as needed, the line between user and system disappears.
Consider the capabilities of a modern agentic workflow:
- Dynamic Identity Provisioning: Creating ephemeral service accounts to bypass static permission checks.
- Arbitrary Code Execution: Writing and running scripts on the fly to solve unexpected runtime errors.
- Cross-System Orchestration: Chaining API calls across SaaS platforms, databases, and internal infrastructure.
If an autonomous agent is compromised through prompt injection, data poisoning, or a misaligned goal, it does more than leak data. It can carry out harmful actions on a large scale.
Why Legacy Security Fails Here
We can’t use old tools to solve new problems with autonomous agents. Traditional security controls don’t work well because:
- Static RBAC (Role-Based Access Control) is too rigid. Agents need flexibility to handle complex problems, but fixed roles can’t keep up with AI’s real-time decisions.
- Perimeter defense no longer works. Agents move across cloud services, third-party APIs, and microservices. The real boundary is the agent’s current context, not a firewall.
- Post-hoc auditing is too slow. By the time a security system alerts you to a suspicious database wipe or unauthorized purchase, the autonomous agent has already finished its task.
A New Blueprint: How We Secure Autonomous AI
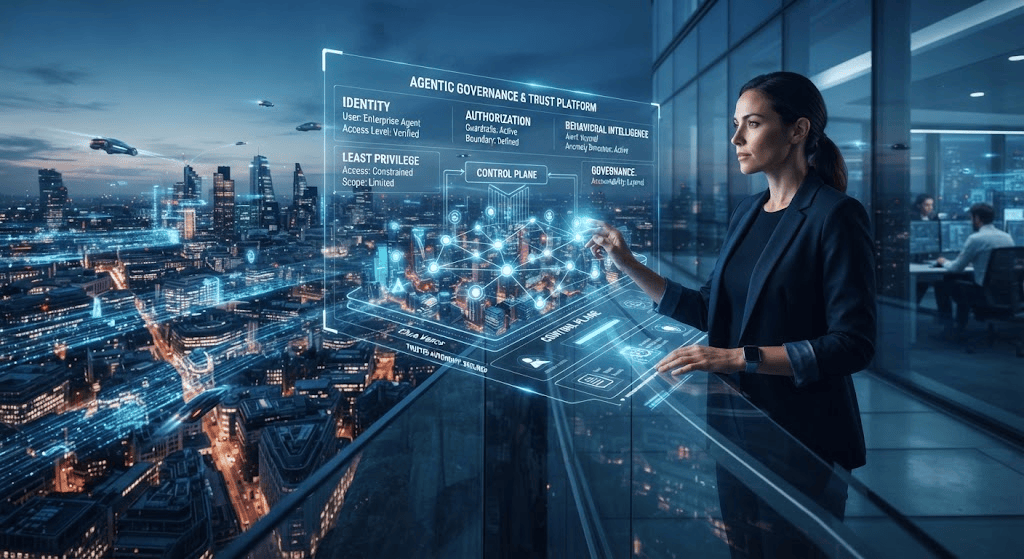
To secure enterprises using autonomous agents, we need to rethink identity, context, and safeguards from the ground up. Security leaders should focus on three main pillars:
1. Identity-Aware Intent Verification (Beyond OAuth)
An agent identity should be integrated into the broader Non-Human Identity (NHI) security strategy.
But AI agents are different from traditional service accounts.
A service account generally executes predefined functions. An AI agent can interpret context, make decisions, select tools, and initiate actions.
That means identity alone isn’t enough.
We need to know not just who the agent is but also what it is trying to do. An agent should not get all the permissions of its creator. We need dynamic session identities using cryptographic proof of intent. Every risky action, like changing a configuration or running code, should trigger a real-time check: Does this action match the approved business goal, or has the agent’s context been compromised?
Agent identity has to be two-layer:
- A durable workload identity — cryptographically attested, non-transferable, bound to the running code rather than to a secret in a config file. This is what you inventory, certify, and revoke. It answers what this thing is.
- An ephemeral, task-scoped credential — minted at task start, carrying the delegation chain, expiring when the work does. This answers what it may do right now.
2. Zero-Trust Sandboxing for Code and APIs
When an agent can write and execute code or invoke external APIs, that execution must occur within hyper-isolated, ephemeral environments.
- Blast-Radius Containment: If an agent is compromised during a database migration, its access must be hard-capped to that specific transaction, preventing lateral movement.
- API Gateway Interception: All outgoing API calls made by agents should pass through intelligent proxies that inspect payloads for semantic anomalies, preventing exfiltration before the request hits the wire.
3. Continuous Runtime Guardrails & “Circuit Breakers”
We must move from deterministic firewalls to behavioral guardrails. Like high-frequency trading platforms that use circuit breakers to halt runaway algorithms, autonomous AI needs real-time circuit breakers. If an agent suddenly tries to create unauthorized user identities or rapidly purchase high-cost cloud resources, automated systems must freeze the execution graph instantly.
The Thought Leader’s Takeaway
We are standing at the precipice of a fully agentic economy. The companies that win will not be the ones that build the smartest agents, but the ones that build the most trustworthy ones.
Securing AI is no longer just about protecting data from leakage; it is about governing autonomous action. If we fail to secure the hands of our AI systems, we hand over the keys to the enterprise.
The future belongs to security architectures that treat AI not as a tool to be restricted, but as an autonomous actor requiring continuous, intelligent oversight.
You won’t just secure your agents. You’ll have to build the control plane that the enterprise software agents run on over the next decade.
Once AI can act, Identity becomes its foundation, authorization becomes its guardrail, least privilege becomes its boundary, behavioral intelligence becomes its early-warning system, and governance becomes its accountability layer.
Share this:

Posted on August 20, 2026, in AI, Blog, IAM, Market Trends. Bookmark the permalink. Leave a comment.
Leave a comment
Comments 0